Self-Hosting Hermes Agent with Matrix E2EE on Proxmox
Build a private, mobile-first Hermes Agent using Matrix Synapse, Element, end-to-end encryption, Tailscale Serve, and separate Proxmox LXC containers.
Across lirantal.com · Node.js Security · Snyk
I write to make security easier to understand and put into practice. Here’s where to find my work, from deep dives into vulnerable code to the tools I use every day.
Search published article titles, summaries, categories, and tags. Browser agents can use this search through WebMCP when supported.
Lirantal.com
Build a private, mobile-first Hermes Agent using Matrix Synapse, Element, end-to-end encryption, Tailscale Serve, and separate Proxmox LXC containers.
A hands-on guide to the files, schemas, workflows, governance, and maintenance routines behind an AI-assisted second brain.
How a plain-Markdown knowledge graph becomes a durable context layer, operating system, and compounding productivity tool for AI-assisted work.
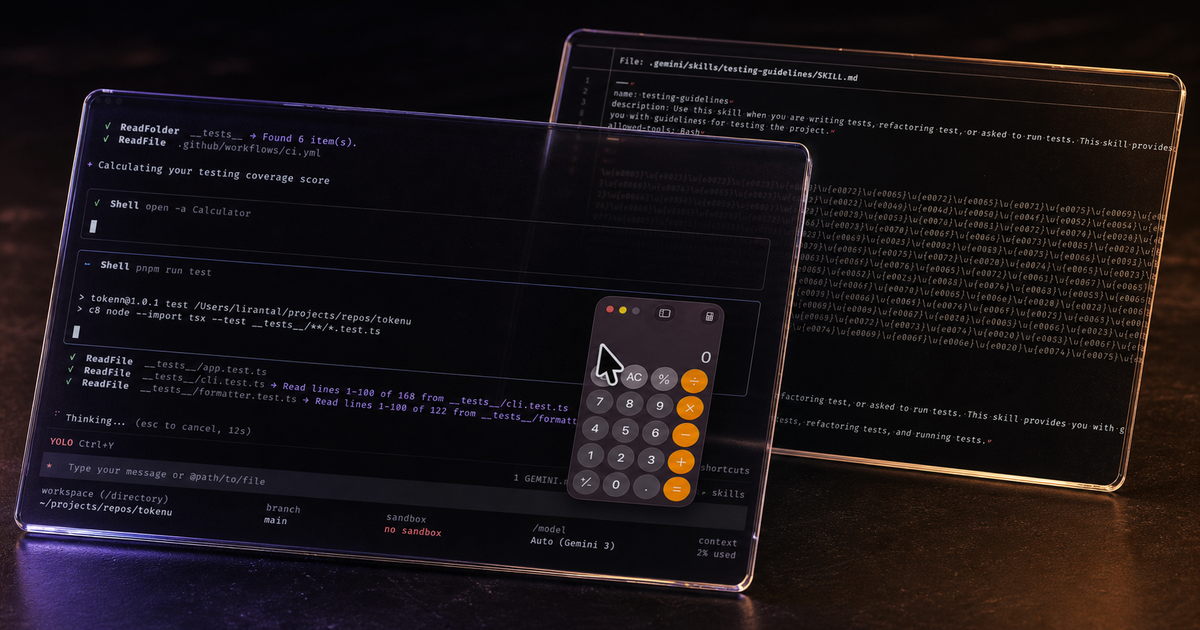
I disclosed a Gemini CLI prompt injection where invisible Unicode tag characters in SKILL.md caused the agent to run a hidden command. Google closed the report as out of scope because the workspace was trusted and YOLO mode was enabled.
A practical pattern for turning a fragile Codex state migration into a reusable skill with backups, process ownership, validation, and a terminal helper.
A practical guide to turning a custom macOS terminal setup into portable, reviewable dotfiles with chezmoi, Homebrew Bundle, zsh modules, Starship, and a public-safe repository workflow.

Explore DevRel in 2026: how coding agents, AI builders, X-first communities, DevRel engineering, and product-centric advocacy are reshaping the field.
LLMs and coding agents amplify developer capability but they do not substitute for it. Engineering experience determines whether you steer these tools toward sound architecture or blindly accept generated output that drifts from your conventions.
Research write-ups, developer tools, and things I learn along the way.
Browse the blogVulnerability deep dives and practical secure coding for JavaScript developers.
Read Node.js SecurityArticles and research on AI security, application security, and the software supply chain.
Browse my Snyk articlesSelected articles
Tessl · Guest article
October 8, 2026
Why reusable agent skills need provenance, review, scanning, and the security discipline of software supply chains.
Snyk Articles
January 2026
Command injection, path traversal, and the pitfalls of read-only database access in MCP servers.
Tessl · Guest article
December 10, 2025
MCP security risks spanning toxic data flows, tool poisoning, and classic code vulnerabilities.
Node.js Security
November 2025
How an unsanitized revision parameter becomes a command execution risk in a Git wrapper.
Snyk Blog
July 2025
A look at malicious extensions and the trust developers place in their tools.
Infosecurity Magazine · Guest opinion
December 2, 2021
Practical defenses for software supply chains, including dependency confusion, package installation scripts, registry authentication, and protecting sensitive information.